ISO/IEC 27001 is the internationally recognized standard for information security management systems, protecting the confidentiality, integrity, and availability of information through risk management.
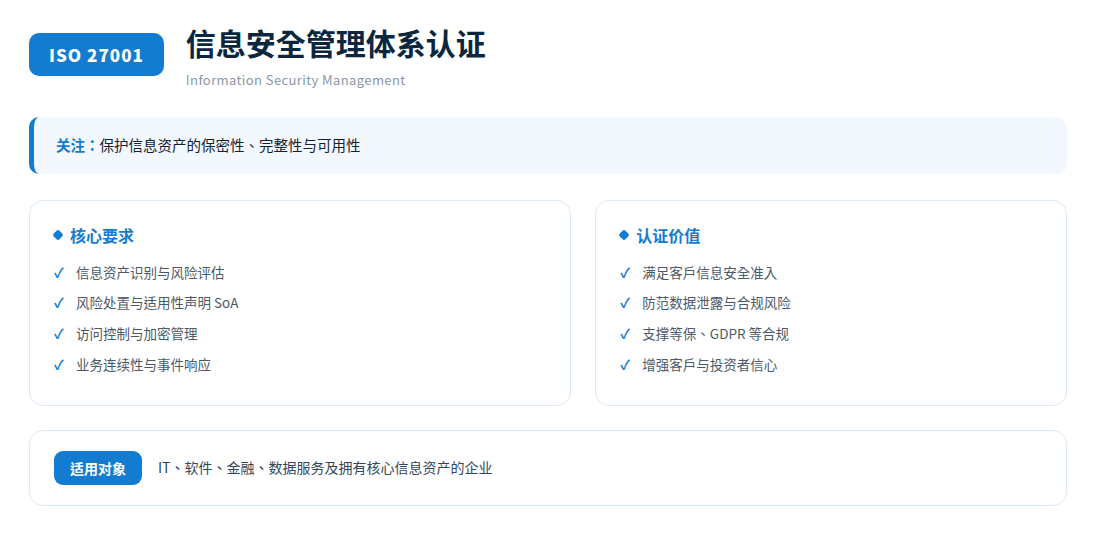
Covers information security risk assessment, selection of controls (Annex A), Statement of Applicability (SoA), and other requirements.
Protect core information assets, meet customer information security requirements, and enhance market competitiveness.
Applicable to all types of organizations that rely on information systems to conduct business.
Contact us for a detailed proposal and quotation, or tell us your needs.
Contact Us